Aaron Dershem
› Principal Software Engineer
I'm drawn to the problems people have written off, the ones that have been stuck for years because they're a pain and nobody owns them. I dig in, figure out how it actually works, and pin down what's actually required to solve it. Twenty-plus years across systems and software, building things that last.
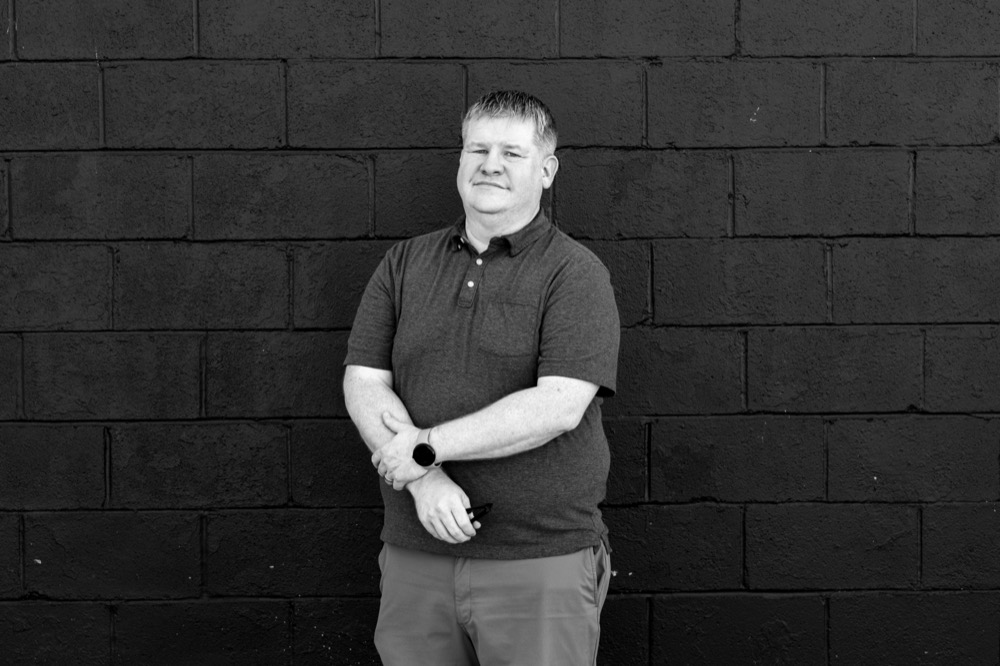
Two decades of building
Once I'm into something, I tend to go all the way in. I learn it properly, build it to last, and stay with it long after the hard part is done, which is how I've ended up owning systems for years that whole teams came to rely on. For most of my career I've also been the senior engineer other people came to when they were stuck.
I spent nearly 19 years at Blackbaud, the last 8 as a Principal Software Engineer, across three teams: monitoring (2018–2022), security automation (2022–2024), and cloud governance (2024–2026).
I architected BBMon, an ASP.NET Core / Angular synthetic-monitoring platform for URLs and certificates that replaced a $200K+/yr commercial tool for about $1,000/month in running costs and grew from 300 to 6,000+ URLs checked every five minutes; the operations center and four product teams used it. It started with an earlier Python certificate monitor of mine that surfaced failures the existing monitoring was silently missing. For seven years I also owned an inherited access-request platform used by every engineering team, a primary source of access-control evidence for PCI and other compliance audits. It came to me with no tests or documentation; I added both and kept refactoring and upgrading it for as long as I owned it.
More recently, I led an enterprise cloud governance effort spanning roughly 110 Azure subscriptions and 60 AWS accounts. That meant guiding a 20-person committee to an approved enterprise tagging policy for security audits and FinOps, and reconciling data across Azure, AWS, and the ServiceNow CMDB to find missing records and inconsistent tags. The findings led to improved data in the CMDB.
Since early 2026, I've been learning agentic development with Claude Code on personal full-stack and geospatial proofs of concept, built to learn the approach rather than to ship. I use a workflow I built where I own the scoping, architecture, and validation, and every merge is gated by automated review, tests, and CI.
Where I've been
-
Apr 2018 – May 2026
Principal Software Engineer at Blackbaud, Inc.
Built internal tools and platforms through the move from colocation datacenters to the cloud: monitoring (2018–2022), security automation (2022–2024), and cloud governance (2024–2026).
- › Architected and built BBMon, a self-service ASP.NET Core / Angular synthetic-monitoring platform for URLs and certificates, with checkers in multiple datacenters. It replaced a $200K+/yr commercial tool for about $1,000/month in running costs and grew coverage 20x, from 300 to 6,000+ URLs checked every 5 minutes. The operations center and four product teams used it to alert on outages and to confirm sites were back online after maintenance (2021–2025).
- › Inherited and owned the access-request platform that every engineering team used, a primary source of access-control evidence for PCI and other compliance audits. Built on ASP.NET Core / Angular / Cosmos DB, it arrived with no tests or documentation; added tests and docs, and refactored and upgraded it throughout (2019–2026).
- › Led an enterprise cloud governance effort across 110 Azure subscriptions and 60 AWS accounts, taking a 20-person committee from security, finance, compliance, and engineering to an approved tagging policy. Built C#/.NET tools that pulled Azure, AWS, and ServiceNow CMDB (configuration management database) data through APIs and KQL to surface missing records and bad tags, which led to tag corrections and improved data in the CMDB, plus Qlik dashboards to track tag compliance (2024–2026).
- › Built a tool that enabled SQL Server Transparent Data Encryption (TDE) across hundreds of databases and managed their encrypted backups, using ASP.NET Core / Angular and PowerShell (2023–2024).
- › Automated application cutovers behind the enterprise web application firewall with a C# tool that turned bulk DNS exports into the CNAME records and certificate installs each cutover needed (2022–2023).
- › Served as the senior engineer people came to when they were stuck: architecture and design reviews, code reviews, technical roadmaps, interviewing candidates, and mentoring junior and mid-level engineers.
-
Apr 2011 – Mar 2018
Software Engineer to Staff Software Engineer at Blackbaud, Inc.
Enterprise monitoring across 3,000+ servers and 40+ product lines, and the internal tools that grew out of it.
- › Unified data from several systems into one inventory of assets across colocation datacenters with an asset-discovery tool built on PowerShell collectors, a C#/.NET API and ASP.NET MVC front end, and a SQL Server backend; it ran in production for 4 years.
- › Designed and built a Python TLS certificate monitor that flagged expiring and misconfigured certificates and routed its alerts into monitoring; testing uncovered site failures the existing monitoring was missing, which led to BBMon.
- › Architected and rolled out enterprise monitoring across 3,000+ Linux and Windows servers supporting 40+ product lines: led the Linux move from Nagios to CA/Broadcom DX UIM and stood up SCOM for Windows as part of a broader monitoring consolidation, designing the gateway topology, agent strategy, and alert routing for application support teams, and ran the monitoring stack day to day.
- › Authored custom SCOM management packs, adopted company-wide, that defined health checks for every product and routed alerts to the owning teams, and maintained and modified a custom C# SCOM connector.
-
Oct 2007 – Apr 2011
Systems Engineer (Linux) at Blackbaud (via eTapestry acquisition)
- › Ran eTapestry's Linux and Solaris production environment, networking, firewalls, NetScaler load balancers, and datacenter buildouts on a 3-person IT team, joining as Blackbaud acquired it; the team's scope later grew to all of Blackbaud's Linux and Solaris infrastructure.
- › Led the infrastructure controls for eTapestry's first PCI DSS audit across 200 Linux servers, built from the ground up: hardening, centralized logging, IAM, network segmentation, and file integrity monitoring. Partnered with external auditors to define scope and pass the initial audit.
-
Feb 2004 – Sep 2007
System Administrator at Radley Corporation
- › Designed and built the SaaS hosting infrastructure for a 30–50-person EDI/SCM software company as its sole IT and infrastructure engineer, reporting to the CEO.
What I'm into
Indy Study Hall
I co-organize indy.sh, a monthly Indianapolis cross-discipline drop-in. Secretly, it's a low-pressure excuse for introverts to get out and find their people. Running since 2016.
Astrophotography
Astrophotography, and really anything worth pointing a camera at the sky for. Always half-waiting on the next eclipse.
Cycling
These days my gravel bike mostly lives on a Tacx trainer, head down and going nowhere fast. It really needs to see the light of day and discover what some of the new trails have to offer.
AV / live production
A portable AV rig I've built up over the years: rack-mounted audio mixing, video switching, projector screen, greenscreen. Built for in-person, hybrid, and livestreamed events, and ready whenever the occasion calls for it.
Let's talk
- Phone
- GitHub github.com/ajdershem
- LinkedIn linkedin.com/in/aarondershem
Email & phone are click-to-reveal to keep scrapers and spammers out.